
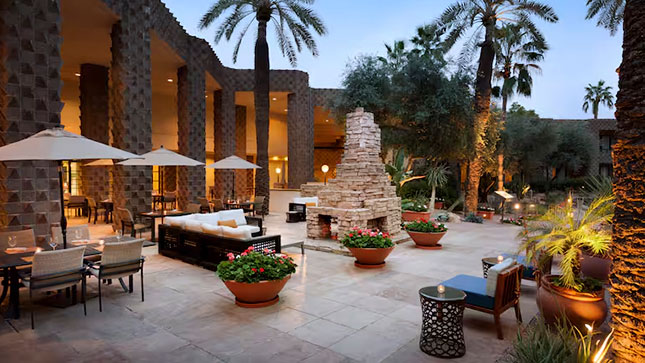
Join us for the 2027 Vulnerability Management Ecosystem Collaboration, Ideation, and Action Conference (VulnCon), co-hosted by FIRST and the CVE Program. The conference will take place March 30-April 2, 2027, at the DoubleTree Resort by Hilton Paradise Valley in Scottsdale, Arizona, USA.
VulnCon brings together professionals from across the vulnerability management and cybersecurity communities to collaborate, exchange ideas, and drive meaningful outcomes. The conference also serves as the annual gathering for the CVE Program's CVE Numbering Authorities (CNAs), bringing together CNA representatives from around the world to discuss program developments, share operational insights, and strengthen collaboration within the CVE ecosystem. Designed to foster engagement across the broader vulnerability management community, VulnCon helps participants gain insights, share best practices, and develop strategies they can apply within their own organizations and programs. A key objective is to deepen understanding of the roles, initiatives, and priorities of major stakeholders while identifying opportunities to amplify collective impact.
VulnCon is open to FIRST members and non-members worldwide who are actively engaged in vulnerability management.
Check out content from the previous VulnCons! VulnCon26, VulnCon25 & VulnCon24
Registration is Open!
-
"Security professionals have many conference options in today's market; however, Red Hat continues to get more value out of the presentations and topics at VulnCon than any other conference. Topics are vetted very well and are almost always relevant to the work we do as a software manufacturer to both proactively and reactively address vulnerabilities.”
-
"What keeps us coming back to VulnCon year after year is the community. The conversations are collaborative, highly technical, and centered around the real challenges vulnerability management teams are facing every day. It's one of the few events where vendors, practitioners, researchers, and industry leaders come together with a genuine focus on improving the ecosystem as a whole.”

Co-Host
CVE
The mission of the CVE® Program is to identify, define, and catalog publicly disclosed cybersecurity vulnerabilities. There is one CVE Record for each vulnerability in the catalog. The vulnerabilities are discovered then assigned and published by organizations from around the world that have partnered with the CVE Program. Partners publish CVE Records to communicate consistent descriptions of vulnerabilities. Information technology and cybersecurity professionals use CVE Records to ensure they are discussing the same issue, and to coordinate their efforts to prioritize and address the vulnerabilities.
Co-Host
FIRST
FIRST is the premier organization and recognized global leader in incident response. Membership in FIRST enables incident response teams to more effectively respond to security incidents - reactive as well as proactive. FIRST brings together a variety of computer security incident response teams from government, commercial, and educational organizations. FIRST aims to foster cooperation and coordination in incident prevention, to stimulate rapid reaction to incidents, and to promote information sharing among members and the community at large.

Diamond
Hinoki
Hinoki (noun), the self-driving exposure management platform for turning findings into fixes. We detect CVEs across cloud and on-premises, relentlessly AI-pentest apps for complex business logic issues, and prioritize using the data already living in your systems. Our agents are outcome-driven, following through on remediations until the fix or compensating control is verified. Attackers don't sleep because they use AI. So should you.