
2027 Program Committee
FIRST is a member driven, non-profit organization with emphasis on information sharing within its global membership as well as the incident response community at large. The Program Committee is a volunteer opportunity, open to non-members and managed through an open call submission process. Program Committee members are selected for their expertise in key areas relating to program objectives, regional balance, and previous program & content committee experience.
About the Program Chair
-
Martijn Van der Heide
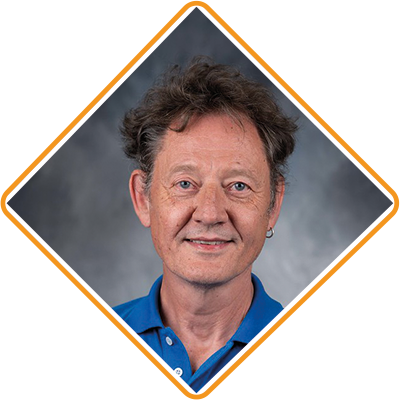 Martijn has been working in the information security field for almost 30 years.
Currently he works as a consultant at the Electronic Transactions Development Agency (ETDA) Thailand, to help improve security further in the country. His role includes incident response, threat intelligence, PKI, training, and consulting. He also authored a number of handbooks and whitepapers, several of which can be found on the FIRST website. One of the other projects he is currently involved in is professionalizing the Thailand National Root Certification Authority (NRCA).
Before that, he worked at Royal Dutch Telecom, KPN, the incumbent telecom provider of The Netherlands, where he set up KPN-CERT which he chaired for 12 years. Then he was invited to move to Thailand in 2014, to join the National CERT (ThaiCERT) team. The National CERT function has since moved to the National Cyber Security Agency (NCSA), and Martijn was asked to take an additional role as advisor for this agency.
Program Committee Overview
Adli Wahid
APNIC
Adli Wahid is a Senior Internet Security Specialist at APNIC with more than two decades of experience in cybersecurity and incident response. He works across the Asia-Pacific region to support cybersecurity capability development, strengthen collaboration among CERTs and CSIRTs, and improve operational cooperation between governments, network operators, law enforcement agencies, and security communities. Prior to joining APNIC, he served as Head of MyCERT (Malaysia Computer Emergency Response Team) from 2006 to 2012. Adli's areas of expertise include cyber threat intelligence, incident response, and Internet infrastructure security. He also served on the Board of Directors of FIRST (Forum of Incident Response and Security Teams) from 2014 to 2018.
Alexander Jaeger
Incident Management and Digital Forensics, Google
Alexander Jäger is a Senior Security Engineer working in the Incident Management and Digital Forensics team at Google. He is active in various open source projects. He studied technical computer science at the University of applied sciences in Mannheim and holds a Dipl.-Ing (FH). Alexander is the former Chair of the board of directors and CFO of FIRST (Forum for Incident Response and Security Teams). If not in front of a computer you might find him doing a swim bike run.
Andreas Brathen
Andreas is a seasoned Cyber Threat Intelligence (CTI) analyst and Threat Hunter (TH) with over 15 years in cybersecurity. He currently specialises in the analysis of adversary tradecraft, providing actionable intelligence for strategic and tactical use, and leading and supporting threat hunting programs, and various intelligence initiatives for mission success.
Throughout his career, Andreas has led multiple teams in threat intelligence, threat hunting and detection engineering. His CSIRT experience includes CSIRT managerial role for multiple organisations, conducting CSIRT maturity assessments, and serving in advisory roles based on frameworks such as SIM3, MRD-IMC, CSF, ISO/IEC 27035, and NIST SP 800-61. Additionally, he is an incident commander and forensic expert in incident response engagements involving advanced threat actors, including nation-state groups (NSGs) and organised crime groups (OCGs).
Angela Wu
Threat Intelligence and Response in Infocomm Media Development Authority, Singapore
Angela Wu is the Director for Threat Intelligence and Response in Infocomm Media Development Authority, Singapore.
She has 20 years of information security & technology experience, working across various sectors including government, banks, technology companies based in Singapore. Aside from leading cyber incident investigations, she has practitioner experience conducting threat analysis, assessment, evaluating cybersecurity risks, impact to the organisation. She conducts briefings, advises on recommended mitigations, solutions to detect & prevent attacks, to senior management on cyber threats and incidents that impact the sector or organisation.
Barry Greene
Akamai Technologies
Barry Raveendran Greene is a pioneering architect of the global internet with over three decades of experience building, scaling, and securing critical infrastructure. Beginning with his invention of foundational DDoS mitigation techniques during Desert Shield/Storm in 1990, Greene has consistently operated at the forefront of network security and operational excellence. He transformed Singapore into a dominant regional internet hub through the creation of STIX, co-founded the Asia-Pacific's premier technical conference APRICOT, and, as Cisco's Chief SP Security Architect, led the globally influential ISP Workshop Program that empowered thousands of network engineers worldwide. Greene co-authored the seminal IETF standard RFC 5575, which defined BGP FlowSpec—now an indispensable tool for DDoS defense—and has held leadership positions at Juniper Networks (Director of SIRT), the Internet Systems Consortium (President), and, most recently, as Principal Architect at Akamai Technologies. Beyond technical innovation, he built the "global trust community" of security professionals whose collaborative, behind-the-scenes coordination has defended against major internet-wide threats, including Code Red, SQL Slammer, and Conficker. His operator-first philosophy and dedication to community empowerment have made him one of the internet's most impactful, if often behind-the-scenes, defenders.
Bekarys Kabi
TSARKA
Bekarys Kabi is Chief Product Officer at TSARKA, a leader in cybersecurity in Central Asia. He leads the Tumar.One bug bounty platform and the TSARKA Products Ecosystem. His work covers product strategy, SOC operations and business development across Kazakhstan and Central Asia. Bekarys works closely with national regulators and government bodies to advance vulnerability disclosure and bug bounty adoption in the region, and engages with international communities including FIRST, ITU and OIC-CERT. He is also the main organizer of KazHackStan, the largest cybersecurity conference in Central Asia, bringing together over 10,000 participants.
Chitpon Jeekhao
Chitpon Jeekhao(CJ) is a cybersecurity expert with over 13 years of experience. His expertise covers security architecture, threat operations, incident response, and GRC, with a focus on building comprehensive security frameworks and strengthening organizational cyber resilience.
Christopher Banda
Malawi Communications Regulatory Authority
Mr. Christopher Ganizani Banda is the Head of the Computer Emergency Response Team (CERT) and works under the Malawi Communications Regulatory Authority (MACRA). He has been at the center of developing and coordinating cybersecurity issues in Malawi, including developing the National Cyber Security and Child Online Protection Strategies and facilitating the designing, establishment, and management of the Malawi National CERT among others. He has been involved in various national and international cybersecurity Policy Forums, and treaties such as ITU, COMESA, SADC, FIRST, Council of Europe, and others. He was the vice Rapporteur for ITU-D Study Group 2 Questions 3/2 (Securing information and communication networks: best practices for developing a culture of cyber security) for the study period 2014-2017. He holds MSc and BSc Degrees in ICT from the University of Malawi, and MSc Degree in cybersecurity from EC Council University, a Certified Network Defender (CND), Certified Ethical Hacker (CEH) and a Computer Hacking Forensic Investigator (CHFI) and Currently studying PhD in cybersecurity with University of Cape Town. He has over eighteen years of technical experience in the ICT sector. The last 12 years have focused on cyber security. He is the CND Scheme Committee Board Member for EC Council
Dace Bulte
CERT.LV
Dace Bulte is a Cybersecurity Analyst at CERT.LV – Latvia’s national cyber incident response team. She specializes in analyzing cyber threats, trends, and developments shaping Latvia’s digital environment. Her work focuses on producing analytical reports on Latvia’s cyberspace, translating complex cyber threat trends and digital security developments into clear, data-based insights that support informed decision-making and strengthen cyber resilience.
Enrico Lovat
Siemens Technology
Enrico Lovat received his PhD from the Technical University of Munich for his research on the topics of usage control and information flow tracking. He joined Siemens CERT in 2016 in the dual role of Incident Handler and Cyber Threat Intelligence Team Lead. In 2022 he moved to Siemens Technology as Principal Key Expert, supervising the research in technologies and innovations for cybersecurity services.
Harish Shankar
Schneider Electric
Harish Shankar is currently working as Director – Head of Product Vulnerability Management in Schneider Electric. In this role, he heads Schneider Electric’s PSIRT Team which is represented as SE - Corporate Product Cyber Emergency Response Team (CPCERT) where he is responsible for defining and governing product vulnerability response. Prior to this role, he handled Product Incident Response and has hands-on experience on Incident Response and Digital Forensics. He also held the positions of Information Security Officer for the APAC region in Schneider Electric.
Jacomo Piccolini
Team Cymru, BR
Jacomo Piccolini joined Team Cymru in 2012 as part of the Outreach Team and is based in Brazil. Prior to working at Team Cymru, he worked at the Brazilian Research and Academic Network, at their Academic CSIRT, and acted as the Academic Coordinator for the Educational School’s security and IT governance curriculum. With 23 years of field experience, Jacomo holds a degree in Engineering and a post-graduate degree in Computer Science and Business Administration. Jacomo is known globally due to his long time involvement in FIRST (The Forum for Incident Response and Security Teams). He is a Liaison Member of FIRST and the team representative for Team Cymru. Jacomo is also Team Cymru representative at OIC-CERT.
Previously Jacomo coordinated hands-on activities for FIRST and is now contributing on the Membership Committee. Jacomo is also known for his work and contributions within several security communities and trust-based groups, serving as an advisor, doing pro bono work and as an elected board member. Jacomo is responsible for Team Cymru's Community Services, including the CSIRT Assistance Program (CAP) and the Data Sharing Partnerships. When possible he returns to education, teaching network forensics and CSIRT security courses, at the post-graduate level, as an invited professor. When not working to make our networks safer places, Jacomo spends time doing his other great love, photography.
James Young
Global Security Strategist at Splunk
As a Principal member of the Global Security Strategist team at Splunk, James brings more than 30 years of cyber security experience across a range of operational, engineering, architecture, and strategy roles. During his career, James has worked across a broad range of industries around the world including Banking, Finance, Telecommunications, Government, Defence and Utilities. Most recently, James' focus has been on helping organisations streamline their security maturity journey though the adoption of modern IT practices and technologies. A key example of this has been James’ work over the last 5 years on helping security operations teams develop and improve detection engineering capabilities as they work towards adoption of approaches such as Detection as Code (DaC). When James is not working, he is chasing winter in the mountains with his family and supporting his two sons as they pursue their competitive snow sports careers.
Jarrod Thompson
CIRT-BS
Jarrod Thompson is a Senior CIRT Analyst at CIRT-BS, the national CIRT of The Bahamas, where he responds to cyber incidents, handles vulnerability management and threat analysis, and supports government agencies and private sector organisations across the country. He came to incident response after more than 19 years in IT, having built and run infrastructure, IT operations, and business continuity programmes before moving into security. He is interested in incident response practice and in sharing experience with teams across the Caribbean.
Jeffrey James Bryan Carpenter
Accuray
Jeffrey Carpenter has dedicated more than 35 years to improving the state of information security in roles such as incident responder, product security officer, information security officer and leader. He currently is the deputy CISO at Accuray, a medical device manufacturer. Jeffrey spent two decades at the CERT® Coordination Center, based at Carnegie Mellon University’s Software Engineering Institute and he also was Senior Director of Incident Response Consulting and Threat Intelligence at Dell Secureworks. Jeffrey has been inducted into the Incident Response Hall of Fame by the Forum of Incident Response and Security Teams (FIRST)
José Alberto Avalos Velez
He has 17 years of experience in the cybersecurity industry, specializing in incident response and Security Operations Center (SOC) services. Throughout his career, he has worked in the manufacturing, healthcare, and financial sectors, as well as for Managed Security Service Providers (MSSPs), where he has led teams and operations focused on incident detection, containment, and recovery. He currently serves as a FIRST (Forum of Incident Response and Security Teams) Liaison and organizes the FIRST Technical Colloquium in Mexico. Additionally, he has served on the program committees for the FIRST Cyber Threat Intelligence conference in Germany and FIRSTCON27. He is passionate about cybersecurity and community collaboration, aiming to strengthen capabilities that help prevent security incidents whenever possible.
Ken Lee
Synology
Ken Lee is a security professional who serves as both an Independent Security Advisor and a Security Consultant at Amazon Web Services. He provides vulnerability response and cloud security governance consulting expertise in his independent role. Prior to AWS, Ken served as the Product Security Officer at Synology, where he led the Bug Bounty Program and the Security Incident Response Team, overseeing critical security operations across the organization. Ken's industry leadership includes serving on the program committee of the Annual FIRST Conference and VulnCon. He has been an active contributor to the security community, sharing his expertise in Product Security and CVE Program management through speaking engagements and community initiatives.
Krassimir Tzvetanor, PhD
Hydrolix/Purdue University
Dr. Tzvetanov has served as a Graduate Researcher at Purdue University for the past six years, focusing on Homeland Security, Cyber Threat Intelligence (CTI), and Influence Operations. Concurrently, he has served as Instructor of Record for graduate-level courses in Cybersecurity and Homeland Security.
For the past three years, Dr. Tzvetanov has also served as Director of Security Engineering at Hydrolix. Prior to this role, he held positions including CTI Lead, Principal Security Engineer and Architect, and Red Team Operator at major technology companies such as Cisco, Yahoo!, and Google. Throughout his career, he has authored training materials, white papers, and academic publications covering distributed denial-of-service (DDoS) attack mitigation and investigation, cyber threat intelligence, privacy, and influence operations. He has also contributed to numerous law enforcement investigations, including providing expert witness testimony in federal court.
Dr. Tzvetanov is an active contributor to the global cybersecurity research and incident response communities. He has served on program committees for ShmooCon, FIRST, NANOG, BayThreat, and the Underground Economy. He is an active participant in several Special Interest Groups within the Forum of Incident Response and Security Teams (FIRST), has contributed to the Honeynet Project, and was a principal organizer of the BayThreat security conference. He also led the Radio Communications Department at DEF CON.
Dr. Tzvetanov holds a Ph.D. and an M.S. in Technology, both with a concentration in Homeland Security; an M.S. in Digital Forensics and Investigations; and a B.S. in Electrical Engineering with a concentration in Radio Communications.
Lisa Lobmeyer
Blue Team Lead
Lisa Lobmeyer Blue Team Lead Lisa is leading Security Research Labs & Allurity’s incident response team. She is an experienced DFIR-Specialist, managing and building teams that help organizations affected by cybersecurity incidents while at the same time tryingto minimize the impact by advancing organizations' Cyber Defense capabilities. She aims to build a bridge from technical issues to real world impact, translating for effective decision-making in management.
Mars Cheng
TXOne Networks' Cyber Threat and Product Defense Center
Mars Cheng is a Head at TXOne Networks' Cyber Threat and Product Defense Center, where he oversees product security incident coordination and response, threat detection operations, and advanced threat research. He also serves as Vice Chairman of the Association of Hackers in Taiwan and is the founder of the HITCON CISO Summit, which he served as General Coordinator from 2023 through 2026, working to strengthen collaboration among the security community, industry, and government while building practical bridges between Taiwan and the international community. In addition, Mars is a visiting lecturer at the NATO Cooperative Cyber Defence Center of Excellence (CCDCOE) and serves as a cybersecurity auditor for the Executive Yuan's National Information and Communication Security Taskforce (NICST), the Ministry of Economic Affairs, and the Ministry of Digital Affairs, contributing to joint efforts by Taiwan and NATO to strengthen critical infrastructure and government cybersecurity.
Mars has delivered more than 65 presentations at international cybersecurity conferences, including Black Hat USA / Europe / MEA, RSA Conference, DEF CON, CODE BLUE, FIRST, HITB, HITCON, Troopers, NOHAT, SecTor, S4, SINCON, ROOTCON, ICS Cyber Security Conference (Asia and USA), CYBERSEC, CLOUDSEC, and VXCON. A dedicated cybersecurity educator, he has taught more than 30 training courses for organizations including Global Cybersecurity Camp (GCC) 2024 and 2026, Taiwan's Cybersecurity Elite Talent Training Program (NICS program), the Ministry of National Defense, the Ministry of Economic Affairs, the Ministry of Education, the Ministry of Finance, HITCON Training, and numerous private enterprises.
His research focuses on ICS/SCADA security, enterprise network security, threat hunting, and emerging cybersecurity issues. To date, he has been credited with more than 10 CVE IDs and has published three papers on applied cryptography in SCI-indexed journals. Mars also served as General Coordinator of HITCON 2021 and 2022, and as Vice General Coordinator of HITCON 2020.
Merike Kaeo
Double Shot Security
Merike Kaeo is CEO and founder of Double Shot Security.
She has over 25 years of experience in pioneering Internet technology deployments and developing strategic security initiatives. Her passion for building cooperation and collaboration between operational, technical, law enforcement and policy sectors in all things related to ‘information security’ has led to many unofficial global liaison roles. In 2007, Merike was instrumental in fostering cooperation and trust among the global operational security community and the Estonian National CERT during the cyber attacks against Estonia.
Merike instigated and led the first security initiative for Cisco Systems in the mid 1990s and authored the first Cisco book on security, Designing Network Security, which was translated into multiple languages and widely used in security accreditation programs. She has held a variety of executive leadership positions and has a deep rooted history in the global Internet community.
Merike is a member of the IEEE, a pioneer member of ISOC and has been an active contributor in the IETF since 1992. She was named an IPv6 Forum Fellow in 2007 for her continued efforts to raise awareness of IPv6 related security paradigms. Merike was appointed to the American Registry for Internet Numbers (ARIN) Board of Trustees in 2016 to serve a one-year term from Jan 1, 2017 to Dec 31, 2017. From 2010-2024 she was an active member on ICANN's Security and Stability Advisory Council (SSAC) and from 2018 through 2021 served as the SSAC Liaison to the ICANN Board.
In recent years Merike has led and contributed to several global threat intelligence sharing initiatives. In 2014 she was part of the EU Network and Information Security (NIS) Working Group 2 that created guidelines and recommendations to promote the sharing of cyber threat information and incident coordination in both the public and private sectors in the EU. She was a founding co-chair of the FIRST Information Exchange Policy SIG.
Merike earned a MSEE from George Washington University and a BSEE from Rutgers University.
Mohammad Makchudul Alam
BGD e-GOV CIRT
Mohammad has been working in cybersecurity for more than a decade. Currently he is an Information Security Specialist at BGD e-GOV CIRT, the national Computer Incident Response Team of Bangladesh, where he runs national threat intelligence operations and incident response for government and critical infrastructure constituents. His role covers coordinated response to ransomware and APT activity, digital forensics, threat intelligence production, and supporting constituent organizations whose security maturity varies widely. He has presented at international forums including the MITRE ATT&CK Community Workshop, and has published in the OIC-CERT Journal of Cyber Security and at IEEE venues.
He is also a Visiting Researcher at the DNS Research Lab, University College Dublin. His research there covers multi-domain threat intelligence fusion, AI-driven security operations for national CERTs and CSIRTs working with limited resources, and threat-informed defense automation for cyber-physical systems, with a particular interest in explainability in security decision making. Before moving into national CERT operations, he worked in IT security and compliance, including PCI DSS, ISO 27001 etc implementation and management. He is an active member of the FIRST CTI SIG and the FIRST AI Security SIG, and holds affiliations with APCERT, OIC-CERT, ICSCoE and ISC2.
Olivier Caleff
CSIRT.FR
Olivier Caleff has been involved in incident and crisis management and CSIRT-related organizations (FIRST, TF-CSIRT, CSIRTs Network, InterCERT-FR) since 1996. He is also and active members of associations of CISOs such as CESIN in France and ECSO in Europe.
He is an advocate of OpenCSIRT Foundation’s SIM3 (Security Incident Management Maturity Model), and a SIM3 Certified Auditor. He organizes and runs cyber exercises for over 10 years.
He is an Individual Member in the FIRST community, and was elected to become a Board of Firectors at FIRST in 2022, before being elected as Chair of the Board in 2025. He contributes to SIG working groups such as the CSIRT Framework.
In 1993 he co-founded APOGEE Communications as CTO, network and security specialist, then as CSIRT Manage. He managed for 5 years the international relationships for ANSSI's CERT-FR – French governmental CSIRT. He previously worked at SANOFI and ERIUM as Cyber Resilience and CSIRT Expert. He now works as interim-CSIRT manager at CSIRT.FR.
Otto Lee
HKCERT
Otto is a cybersecurity leader with over 20 years of experience in cybersecurity, cloud security, data protection and privacy, incident response, security governance, compliance, and operational resilience. His career spans leadership roles across the technology and financial services sectors, where he has built deep expertise in aligning security strategy with regulatory, operational, and business priorities.
As Head of HKCERT, Otto leads cybersecurity service strategy, incident response coordination, and threat alert operations, while working closely with regulators, critical Internet infrastructure operators, industry stakeholders, and international organisations to strengthen cyber resilience and collaboration.
Prior to HKCERT, he served as Security Assurance Lead for APAC New Markets and Region Expansion at Amazon Web Services (AWS), where he led security assurance efforts across the region and advised on cloud security, cybersecurity, data protection, privacy, compliance, and operational resilience. He played an important role in supporting regional expansion initiatives and engaging regulators on security and privacy matters.
Earlier in his career, Otto held regional security and compliance roles in the financial services sector, where he developed global policies and standards, led compliance reviews, supported regional incident response, conducted APAC-wide assessments, and delivered security awareness programmes. He also has 4 years of working experience in Mainland China, where he was responsible for matters relating to intellectual property rights, data privacy, legal and regulatory compliance, site security, and business continuity.
Widely recognised as an industry expert, Otto is a frequent speaker at universities and cybersecurity conferences, an active contributor to professional associations, and a holder of multiple industry certifications, including CISSP, CISA, CCSP, CDPSE, CSSLP, and GLEG.
Ouattara Zié Alhassane
Côte d’Ivoire’s National Cybersecurity Agency (ANSSI)
OUATTARA Zié Alhassane is an Ivorian cybersecurity expert and currently serves as Head of the Security Operations Center (SOC) Department at Côte d’Ivoire’s National Cybersecurity Agency (ANSSI). He specializes in security operations, cyber threat detection and incident response, cyber crisis management, and ethical hacking, with solid experience in leading SOC operations and coordinating cybersecurity teams. He holds a Master’s degree in Computer Science, specializing in Management Information Systems (MIAGE), and is an EC-Council Certified Ethical Hacker (CEH v11). Through his current responsibilities, he contributes to strengthening Côte d’Ivoire’s national cybersecurity capabilities and enhancing the resilience of information systems against evolving cyber threats.
Rick Logan-Stanford
TT-CSIRT
Rick Logan-Stanford
Cyber/ICT Security Specialist, TT-CSIRT (Trinidad and Tobago Computer Security Incident Response Team)
Rick Logan-Stanford is a cybersecurity professional with over a decade of experience securing complex systems and responding to evolving digital threats. At TT-CSIRT, his work spans incident response, digital forensics, vulnerability assessment, and network security, with a growing focus on cyber law, cyber diplomacy, and the geopolitical dimensions of cyberspace.
Rick approaches cybersecurity through a wider lens, one shaped by landmark incidents like Stuxnet, SolarWinds, and NotPetya, where technical breaches escalate into questions of sovereignty, attribution, and international law. He champions an approach grounded in legally sound attribution, ethical restraint, and the protection of civilian systems, even amid active conflict in cyberspace.
A regular voice on the international circuit, Rick has presented research on malicious code-signing certificates at FIRST.org's Technical Colloquium in Amsterdam, discussed AI-driven incident response in Mexico City, and spoken on artificial intelligence and cyber deception at CyberWeek@LAC4. He holds a certification in Legal Aspects of E-Commerce from UNCTAD and continues to bridge technical depth with policy and diplomacy across Latin America and the Caribbean.
Ruben Olague
Ruben is a cybersecurity leader with more than two decades of international experience in cyber resilience, incident response, investigations, and risk management across the telecommunications, government, and financial sectors. He has led global and regional teams responsible for cyber investigations, fraud and ethics inquiries, cyber readiness, crisis management, and large-scale cyber exercise programs, helping organizations strengthen their operational resilience against evolving threats.
He holds a degree in Information Systems Engineering and an MBA, complemented by several professional diplomas and certifications, including CISSP, EnCE, GSTRT, and GCIH.
Based now in Madrid, after some seasons in Mexico and Dublin, Ruben is passionate about building resilient organizations, fostering international collaboration within the cybersecurity community, and mentoring the next generation of security professionals. Outside of work, he enjoys hiking, OCR (obstacle course racing), and spending time with his family.
Shin Adachi
FIRST
Shin Adachi is a Silicon Valley–based incident response professional with extensive international experience across the United States, Japan, and Europe. Specializing in threat analysis, vulnerability assessment, and organizational resilience, he helps his business customers strengthen their security posture before, during, and after critical incidents. Alongside his advisory work, Shin is an entrepreneur holding stakes in multiple entities, including his own cybersecurity business through which he provides strategic, experience-driven guidance to organizations worldwide. A long-standing contributor to the global security community, he previously served as FIRST Education Committee Chair and continues to support other FIRST committees and special interest groups. His work and perspectives have been featured at leading security and technology forums, such as RSAC, ISC2, ISACA, and UE. Shin holds numerous industry certifications, including CISSP, CCSP, CISM, CISA, PMP, and AI Agent Security Specialist, AI Data Security Specialist, and Security Awareness Specialist certified by Proofpoint, reflecting his commitment to staying at the forefront of an evolving cybersecurity landscape.
Stephen Cudjoe-Seshie
Cyber Security Authority
Stephen is a technology leader with over twenty-one years of experience in ICT infrastructure strategy, planning, design, deployment, and operations. He is the Acting Deputy Director-General at the CSA, responsible for technical operations encompassing the national CERT, critical information infrastructure protection, cybersecurity technology standards development, and law enforcement liaison activities.
Susan Ballestero
USBank Europe
Susan Ballestero is a Principal Security Engineer at USBank Europe. Originally from Costa Rica and currently based in Ireland, she holds a Master’s degree in IT Project Management from the Universidad para la Cooperación Internacional. Susan possesses over a decade of cybersecurity experience, specializing in incident response, digital forensics, malware analysis, ransomware investigations, and threat research. An active industry speaker, she has presented her research on ransomware at major global forums, including FIRSTcon, FIRST Puerto Rico, and FIRST Kuala Lumpur. Her professional background also includes participation with Tripwire initiatives, alongside holding GIAC Certified Forensic Examiner (GCFE), CompTIA Security+, and CAPM certifications.
Takayuki Uchiyama
Panasonic PSIRT
Takayuki Uchiyama is a member of Panasonic PSIRT. Main roles are the handling of vulnerabilities, creating and conducting product security training to product developers and aiding product development teams. Aside from his role in Panasonic, Takayuki has been a CVE Board Member since 2016.
Thomas Millar
Special Projects, CISA Cybersecurity Division
Thomas R. (Tom) Millar has served in the Cybersecuirty and Infrastructure Security Division (CISA) since 2009, working to strengthen the nation’s cyber defenses and resilience against emerging threats.
His work has included increasing the level of public, private and international partner engagement, and supporting initiatives to improve information sharing, such as the standardization of the Traffic Light Protocol.
As the Senior Advisor for Special Projects within CISA’s Cybersecurity Division, he works across the agency on emerging risks, strategic initiatives, and process improvements.
Prior to his cybersecurity career, he served as a linguist with the 22nd Intelligence Squadron of the United States Air Force.
Mr. Millar holds a Master’s of Science from the George Washington University and is a Distinguished Graduate of the National Defense University’s College of Information and Cyberspace
Tim Myers
NCSC New Zealand
Tim Myers is the Principal Advisor for Incident Response in the Pacific Partnerships Team at NCSC New Zealand, where he focuses on delivering meaningful and impactful cyber capacity building in the region. Tim also served as a Digital Forensic Analyst within the New Zealand Police where he conducted digital forensic investigations related to serious crime, fraud and cybercrime. Building on his experience, Tim is dedicated to improving cyber security capabilities in the Pacific through fostering Pacific-led initiatives and capacity building activities.
Timo Porjamo
CSC.FI / Funet CERT
Timo is a seasoned IT security professional with more than three decades of experience in cybersecurity and incident response. He began his career in the early 1990s as a Unix system administrator, later specialising in the design, operate, and security of Unix and network security monitoring and analysis environments. He currently leads a CSRIT team and continues to work at the intersection of technical security, incident response, and the development of mature security teams and practises.